Are You Really PCI Compliant?
October 23, 2026
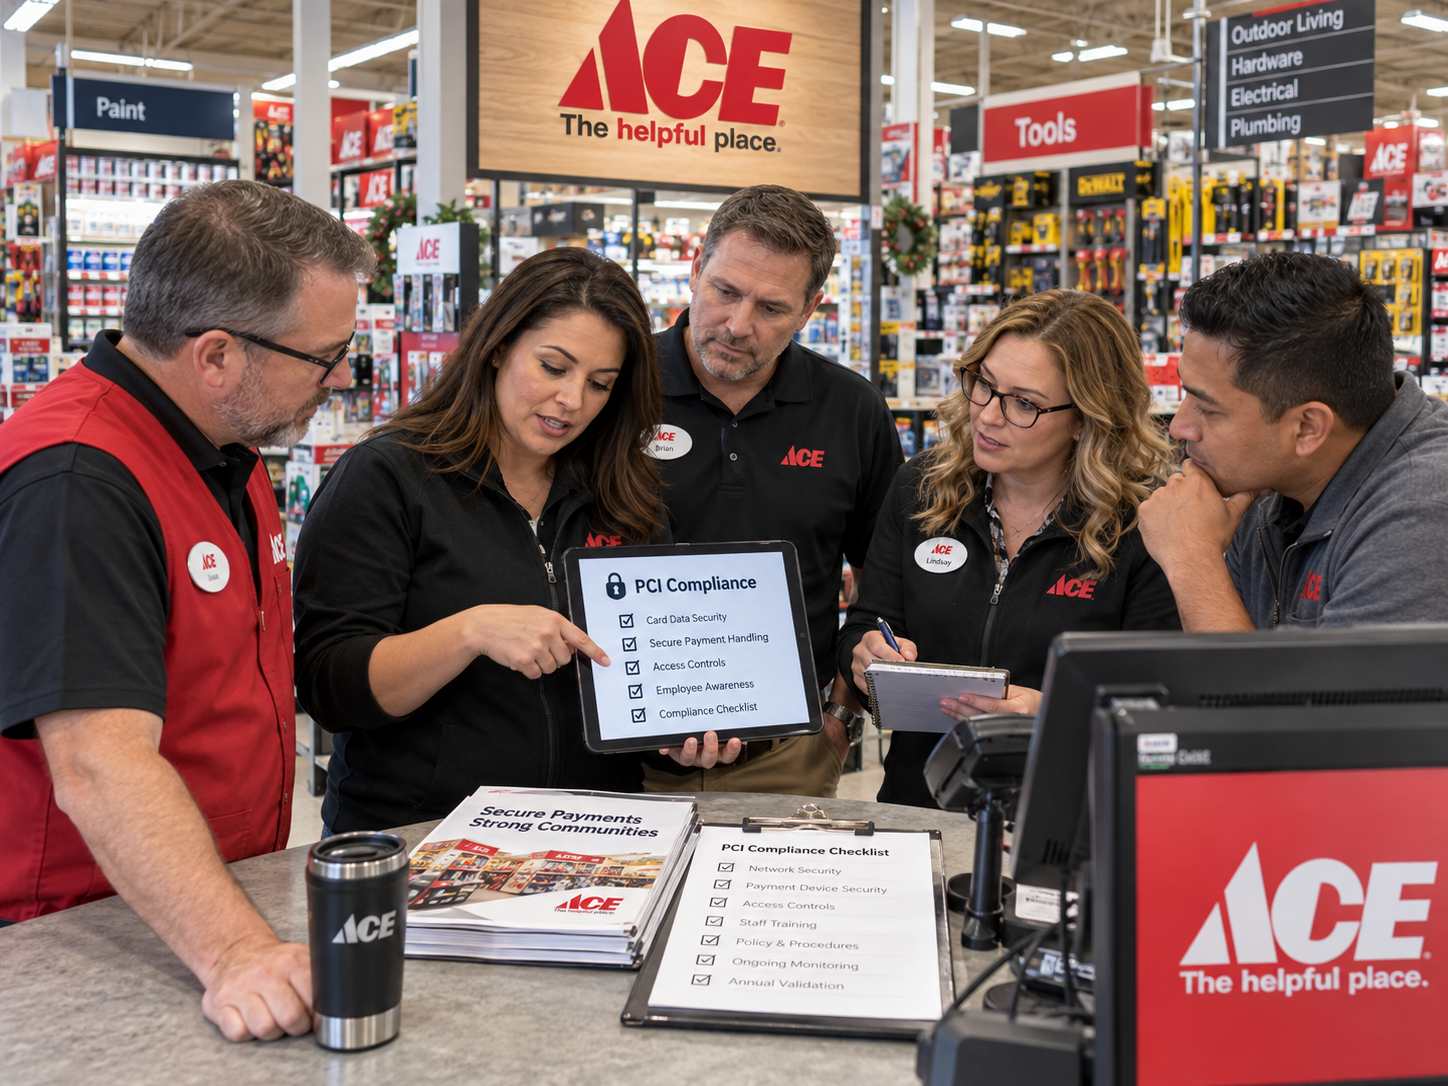
Take the 3-Question Litmus Test
We’re in the midst of Cybersecurity Awareness Month, which makes this a good moment to ask a question every Ace owner should be able to answer with confidence: is your store actually PCI compliant?
Lots of Ace stores tell us they are. Far fewer actually are. That gap rarely matters on a normal day, which is exactly why it is easy to overlook. It matters a great deal on the day a card breach is discovered.
Why PCI Compliance Matters for an Ace Business
The Payment Card Industry Data Security Standard (PCI DSS) applies to every business that accepts Visa, Mastercard, American Express, or Discover cards, and your merchant agreement requires you to follow it. Most Ace stores are small-volume (Level 4) merchants, which means you certify your own compliance. Nobody audits you in advance.
That is the catch: as a Level 4 merchant, nothing bad happens if you are out of compliance until a data breach occurs. Then the question is no longer whether you checked the boxes; it is whether you can prove you were doing what you attested to.
It is also worth remembering that a passing score in a compliance portal is not the same as being secure. PCI sets the minimum standard for protecting the most sensitive information in your business. “Checkbox compliance” is not a substitute for real security.
The PCI Compliance Litmus Test
Answer these three questions honestly. If the answer to any of them is “no,” your store is not PCI compliant today.
- Do you have current, documented policies on file? You should have an Information Security Policy, an Incident Response Plan, a network diagram, and a data-flow diagram, all on file and up to date.
- Has every employee completed cybersecurity training? All staff should complete Ace Learning Place Module 100: Cybersecurity Basics (requires login) when they are hired and again every year. The course is updated every November, and Ace Learning Place keeps the training records for you.
- Is your attestation current? You should have completed your PCI self-assessment through an approved compliance portal, such as SecureTrust or SecurityMetrics, and re-attested within the last 90 days. Most portals require you to re-attest every 90 days, along with any required quarterly network scans.
What Can Happen After a Breach?
- The card brands will investigate. Expect a forensic audit of your business by the major card brands: American Express, Discover, MasterCard, and/or Visa.
- You could lose the ability to accept cards until the deficiencies are fixed, effectively putting your store on a cash-only basis.
- You could face significant fines and costs. Card-brand assessments, forensic investigation fees, and the cost of reissuing compromised cards can be passed through to your business by your processor.
- Your cyber insurance may not pay. A carrier may deny your claim if you cannot pass a compliance audit.
Two Common Misperceptions
“Epicor encrypts my card transactions, so I’m covered.” Epicor’s end-to-end encryption (E2EE) does a very good job of protecting card data and reduces your risk. It is not a PCI-listed point-to-point encryption (P2PE) solution, though, so it does not take your store out of scope. Your network, passwords, computers, and people still count.
“My compliance portal says I’m compliant.” A portal records your answers and schedules your scans. It does not secure your network, configure your POS, or train your staff. If the answers you gave are not true in practice, the portal result will not protect you. We cover this in more detail in Understanding PCI Compliance Validation Portals.
Take the Test Today
Take two minutes and run through the three questions above. If you answered “no” to any of them, here is where to start:
- Policies: Download the DilSe.IT Information Security Policy and Incident Response Plan guidelines from AceNet (requires login) and tailor them to your business. Ask your IT provider for a current network diagram and data-flow diagram.
- Training: Assign Ace Learning Place Module 100: Cybersecurity Basics(requires login) to every employee, starting with anyone who has not completed it in the last 12 months.
- Attestation: If you do not have a compliance portal account, set one up. Stores on the Ace Bankcard Program can use a portal such as SecureTrust; Epicor EPX customers have access to SecurityMetrics through Epicor.
Not sure how your store measures up, or want help closing the gaps? DilSe.IT is Ace’s cybersecurity training partner, and we help Ace retailers nationwide get and stay PCI compliant. Contact us today!